
Risk & Quality
CppDepend for Security Leaders
Catch structural vulnerabilities, identify unsafe memory usage patterns, enforce security policies.
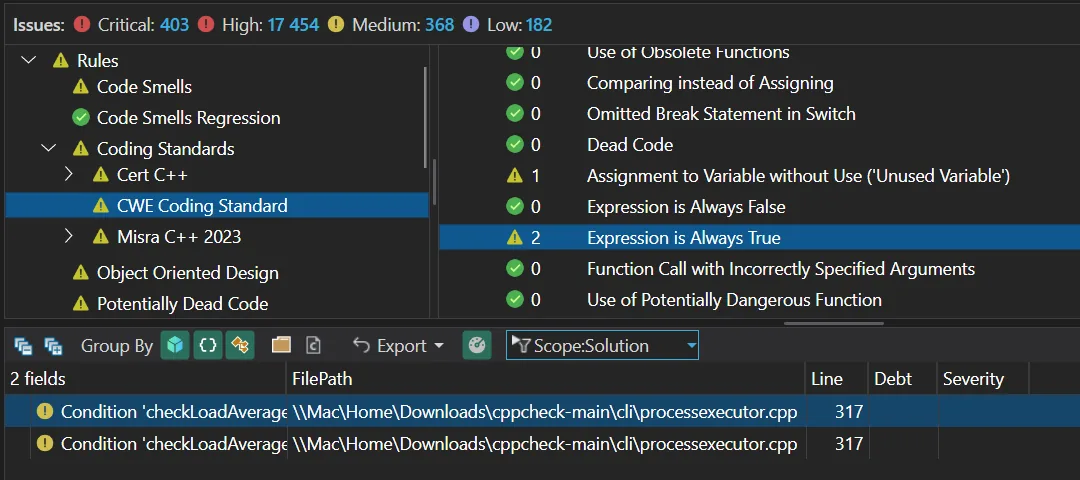
Catch structural vulnerabilities
The most dangerous vulnerabilities are structural: they're built into how the code works, not just what it does wrong on one line. CppDepend's rule set mapped to CWE detects vulnerability classes — injection-prone patterns, weak error handling, dangerous API usage — across the entire codebase, on every build.
Security review stops being a periodic event and becomes a continuous property of the pipeline.
- Rule set mapped to CWE vulnerability categories
- Whole-codebase scanning on every build
- Severity-ranked findings for triage
- Continuous enforcement through CI quality gates
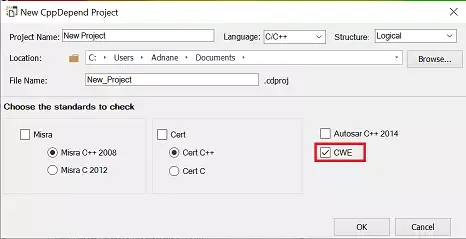
Identify unsafe memory usage patterns
Memory safety is where C/C++ security is won or lost. CppDepend's CERT C/C++ rule support targets exactly the patterns that lead to buffer overflows, use-after-free, leaks and undefined behavior — with each finding explained and located.
Combined with CQLinq, you can write custom queries for your own forbidden patterns: banned functions, unchecked return values, raw pointer usage in modules that should be memory-safe.
- CERT C/C++ memory-safety rules built in
- Detection of leaks, overflow-prone and dangling-pointer patterns
- Custom CQLinq rules for project-specific banned APIs
- Trend tracking to prove memory-safety improvement
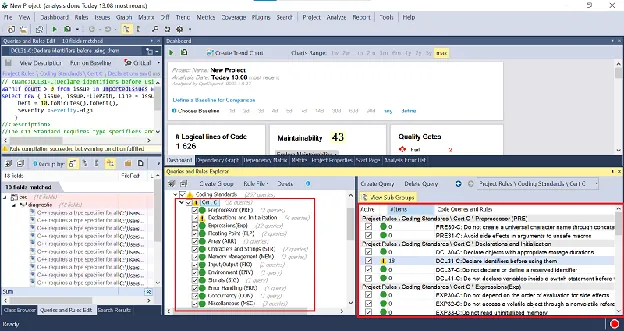
Enforce security policies
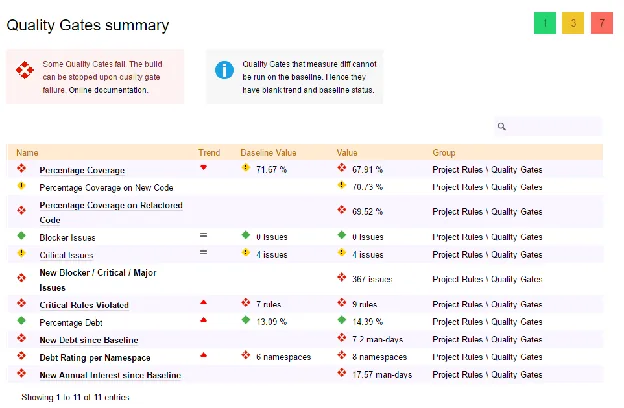
A security policy only works if violating it has consequences. CppDepend turns your security rules — coding standards, banned APIs, required review zones — into enforced gates: code that violates the policy simply doesn't pass the pipeline.
Policies are expressed as versioned CQLinq rules and reports document compliance automatically, giving security leadership both enforcement and evidence.
- Security policies expressed as enforced quality gates
- Versioned rule files shared across all teams
- Automatic compliance evidence for security reviews
- Integration into the release pipeline, not alongside it
See what CppDepend finds in your code
Download the free trial and run a full analysis on your own codebase in minutes.